About NIS2 Advisory
A NIS2 preparation service, made by an IT and security company in Cluj for business owners who want to know exactly what to do, in which order and with what evidence.
What it is
NIS2 Advisory is the preparation side. On this site you have the public tools: check whether the law applies to you, estimate your level and see the roadmap with every obligation and deadline. With us you go further: classification, the inventory, policies that are actually applied, the evidence file, an honestly completed self-assessment and the remediation plan.
We stop at the audit’s door. The audit is done by a DNSC-certified auditor, independent from us.
Why only preparation
The law requires the auditor to be independent from whoever helped you prepare: it cannot be the one providing you security services, cannot have a contract on the audited system, and cannot do more than three consecutive audits at the same company (OUG 155/2024, art. 58 (3)).
Of the two roles we chose the first. It is the role in which we can stand next to you for months, go into systems and procedures, write and correct. The auditor has to come from outside and find everything in its place.
How we work
Six steps, in the order they happen. Each one ends with something you can show.
-
The 30-minute call
Which sector, which size, what you already have, what worries you. You leave with a list, not a quote.
-
Classification and level
We confirm sector, size and group, estimate the risk level and, if you are not registered, guide you through the NIS2@RO notification and the risk assessment.
-
The inventory and the policies
The asset inventory, the risk register, the roles and the policies that are actually applied, written in your company’s language, not copied from a template.
-
The evidence
For every control scored 3 or more, the proof that supports it: the export, the report, the record, the log. A single file, dated.
-
The self-assessment and the plan
We complete the self-assessment for your level together, with justifications you can stand behind, and write the remediation plan with owners, deadlines and closing evidence.
-
Handover
The file stays yours. You sign and submit to DNSC; we stay around for questions. You pick the auditor from the list DNSC publishes.
Who answers
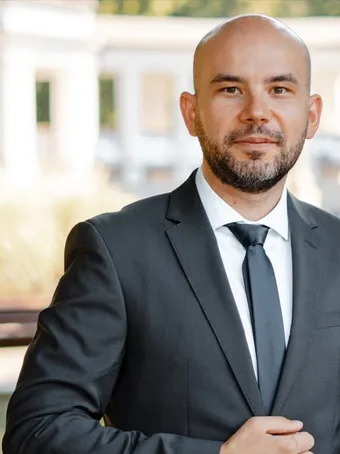
Marius Galmati
Founder of BitUp Technology, cybersecurity and compliance consultant
He came from ISO 27001 audits, internal and external, in a Fortune 500 corporation, where he worked on policies, governance, continuity and endpoint security. Before that, a systems administrator at companies in Cluj: firewalls, backup, virtualisation, user directories.
He reads every control through the auditor’s eyes and translates it into what it means for your company: who does it, when, with what proof. He personally answers every call.
BitUp Technology
BitUp Technology SRL is an IT services, security and compliance company in Câmpia Turzii, Cluj county, Romania, founded in 2020: IT administration for small and medium businesses, security, backup and recovery, cloud, software development. NIS2 Advisory is its product for NIS2 preparation.
What we do not do
- We do not perform the cybersecurity audit required by law and we do not subcontract it: you choose it, from the DNSC list.
- We do not issue certificates or compliance “labels”: “DNSC compliant” or “CyFun verified” have no legal basis in Romania.
- We do not submit anything to DNSC on your behalf: you sign and submit, we prepare and check.
- We do not promise deadlines the law does not have: where the order is missing (audit frequency), we say so.
Let’s see where you stand
Thirty minutes, free, no strings. You come with what you know; you leave with the next steps.